Note: This post was written in February 2020. Some screens and steps may have changed since then.
Introduction
With more organizations moving to the cloud, a common question that we see from Nintex developers is: “I used to use Query LDAP to retrieve my users from Active Directory. Now that my users are in Azure, how do I retrieve them?”
Query LDAP is an out-of-the-box (OOB) action in Nintex Workflow for SharePoint on-premises. With minimal configuration, it allowed developers to grab users from an on-premises Active Directory (AD) group.
The problem a lot of users face when they start using Nintex Workflow for Office 365 or Nintex Workflow Cloud (NWC), is that there’s no equivalent action to Query LDAP (at the time of writing this article).
In this blog post we will learn how to leverage Microsoft Graph API to retrieve the members of an Azure AD group.
We will build our workflow using Nintex Workflow for Office 365. However, you can apply the same concepts you’ll learn today, if you’re building an NWC workflow.
Our Approach
The end result of our workflow will be a collection of users’ principals, that you can use however you prefer. The collection will look as follows:
["JohannaL@M365x037951.OnMicrosoft.com","LeeG@M365x037951.OnMicrosoft.com","RaulR@M365x037951.OnMicrosoft.com","DeliaD@M365x037951.OnMicrosoft.com"]
To get there, we’ll follow the steps below:
- Azure AD:
- Get your Azure AD group’s ID
- Register a new Azure AD app
- Generate a new secret for the app
- Grant the app access to the Graph API
- Nintex Workflow:
- Use the Azure AD app ID and secret, and your tenant ID to get a bearer token
- Retrieve the access token from the bearer token
- Use the access token to call the Graph API and get the users from your Azure AD group
- The users will come back in a JSON object
- Parse the JSON object and generate a collection of user principals
Let’s get started
In this tutorial, we will retrieve the members of an Azure AD group in a JSON object. From the JSON object we will retrieve the userPrincipleName property of each member. Once we have the members’ JSON object, it’s straightforward to grab any other user properties like display name, email, phone number etc.
Our group name is “sg-Engineering” and it has the following four members:

Get your Azure AD group’s ID
- Go to Azure AD: https://portal.azure.com/ -> Azure Active Directory
- In the left navigation bar, click Groups
- Click on your group’s name
- Save the Object Id to a text editor.

- This is your group ID.
Register a new app in Azure Active Directory and grant permissions
- Go to Azure AD: https://portal.azure.com/ -> Azure Active Directory
- Register
a new app
- In the left navigation bar, click App registrations -> New registration

- Fill-in the fields as follows:
- Name: give a name to your app
- Supported account types: select the option that best suits your requirements. For this tutorial, we’ll select “Accounts in this organizational directory only”
- Redirect URI: Web – http://localhost

- Click Register at the bottom
- Save the Application ID and Tenant ID to a text editor

- Generate
client secret
- Click Certificates & secrets -> New client secret

- Fill-in the fields:
- Description: give a description to your client secret
- Expires: choose when you’d like the secret to expire

- Click Add at the bottom
- Save the Client Secret to a text editor

- Grant your app permissions to Microsoft Graph
- Click API permissions -> Add a permission -> Microsoft Graph -> Application permissions

- Select the following permissions:
- GroupMember -> GroupMember.Read.All
- Users -> User.Read.All
- Click Add permissions at the bottom
- You’ll need the Global Admin to click on Grant admin consent

- You’ll need the Global Admin to click Yes for the confirmation pop-up
- The permission’s Status should change from “Not granted” to “Granted”
- Click Add a permission -> Azure Active Directory Graph (at the bottom)-> Delegated permissions
- Select User -> User.Read
- Click Add permissions at the bottom
- You’ll need the Global Admin to click on Grant admin consent
- You’ll need the Global Admin to click Yes for the confirmation pop-up
- The permission’s Status should change from “Not granted” to “Granted”

Build the workflow
- We’ll start by creating a new blank workflow
- Then we’ll create the variables
- Click on Variables in the top bar, then add new variables as shown below:

- Then we will set the variables to the values we saved from Azure AD:
- Add a Set Workflow Variable action and set the variables as follows:
- varTxtAppID: Application ID you saved earlier
- varTxtTenantID: Tenant ID you saved earlier
- varTxtAppSecret: Client Secret you saved earlier
- varTxtGroupId: Group ID you saved earlier
- Add a Set Workflow Variable action and set the variables as follows:

- Now we will get the bearer token
- Add a Web Request action
- Set the properties as follows:
- URL: https://login.microsoftonline.com/{Variable:varTxtTenantID}/oauth2/token
- Method: POST – content type: application/x-www-form-urlencoded
- Body: Content radio button – grant_type=client_credentials&client_id={Variable:varTxtAppID}&client_secret={Variable:varTxtAppSecret}&resource=https://graph.microsoft.com&scope=user.read
- Username: your username
- Password: your password
- Store response content in: varTxtBearerTokenJson
- Store http status code in: varIntgrResponseCode

Once this action runs, we will have retrieved the bearer token in a JSON format and saved it to our variable varTxtBearerTokenJson. This is how the bearer token will look:

From the bearer token, we want to retrieve the access token. The easiest way to do this, is to store the bearer token in a dictionary, then retrieve the value for the key “access_token”
- Add a Set Workflow Variable action and
set it as follows:
- varDctnryBearerTokenJson: varTxtBearerTokenJson

- Add a Get An Item From A Dictionary action and set it as follows:
- Dictionary: varDctnryBearerTokenJson
- Item name or path: access_token
- Output: varTxtAccessToken

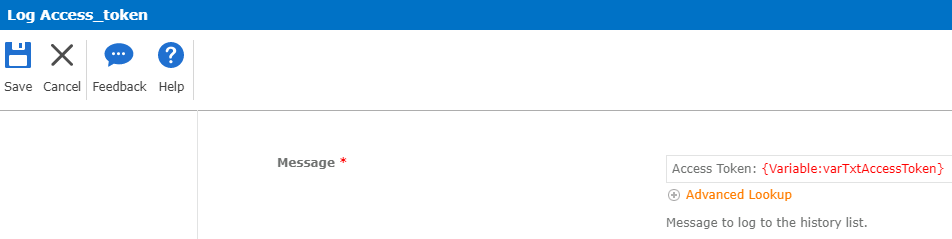
- Log access token – to make sure we retrieved it successfully
Note: You will not see the full access token in Workflow History due to the character limit. You can Email it to yourself to see the full token.
- Now, let’s call the Graph API and get the members
- Add a Web Request action
- Set the properties as follows:
- URL: https://graph.microsoft.com/v1.0/groups/{Variable:varTxtGroupId}/members
- Method: GET
- Header name (key): Authorization
- Header value: Bearer {Variable:varTxtAccessToken}
- Username: your username
- Password: your password
- Store response content in: varTxtUsersJson
- Store http status code in: varIntgrResponseCode

Once this action runs, we will have retrieved the group members in a JSON format and saved the object to our variable varTxtUsersJson. This is how the users’ JSON will look:

- Now that we got the users, we need to extract the property userPrincipalName. We will retrieve it
using Regex.
- Add a Regular Expression action
- Set the properties as follows:
- String: {Variable:varTxtUsersJson}
- String operation: Extract
- Pattern: (?<=(userPrincipalName\”\:\”))[^”]+
- Thanks to Tomasz Poszytek for providing the regex.
- Note: https://regexr.com/ is a great tool to test your regex before using it in your workflow.
- Output: varCollUserPrincipalNames

- Let’s confirm that we retrieved the users successfully
- Add a Send an Email action
- Set the properties as follows:
- To: your Email address
- Subject: Users
- Body:
Response Code: {Variable:varIntgrResponseCode}
Users Json: {Variable:varTxtUsersJson}
Users Collection: {Variable:varCollUserPrincipalNames}

- That’s it! Now run the workflow.
- You should receive an Email with the following:
- Response Code of 200
- Your AD group members in a JSON format
- A collection of your AD group members’ user principal names

Conclusion
Microsoft Graph API allows you to access tremendous amount of data in Microsoft 365. In this tutorial we used the API to retrieve Azure AD group’s members. However, the API can be used for a lot more than that. The tricky part here was to get the access token. Now that you learned how to get the token, check out the Graph API and see all the cool things you can do.
References
- Microsoft Graph API – Get access token without a user:https://docs.microsoft.com/en-us/graph/auth-v2-service
- Microsoft Graph API – List members end point:https://docs.microsoft.com/en-us/graph/api/group-list-members
Find this article and other interesting reads on DevFacto’s blog.